Skip to content
Envescent Envescent

An investment in security pays dividends of continuity.

  • Home
  • AI
    • Consulting
    • Generative AI
    • Optimization
    • Security
  • Automation
  • Cloud
    • Amazon Web Services
    • Consulting
    • Engineering
    • Microsoft 365
    • Migration
    • Security
  • Cybersecurity
    • Assessments
    • Compliance
    • Consulting
    • Digital Forensics
    • Endpoint Protection
    • Glossary
    • Healthcare
    • Incident Response
    • Law Firms
    • Monitoring
    • Pen Testing
    • Policy
    • Threat Analysis
    • Virtual CISO
  • Finance
  • Get Help
  • IT
    • Data Protection
    • IT Consulting
    • Linux
    • Research
  • Training
    • Cybersecurity
  • About
    • Case Studies
    • How We Work
    • Methodology
    • Privacy Policy
    • Service Menu
    • Standards
    • Terms of Service
  • Insights
  • Navigation

Home » cybersecurity » The importance of multi-factor authentication to secure your accounts

By Alexander G Chamandy · Published March 6, 2020
Multi-factor authentication

The importance of multi-factor authentication to secure your accounts

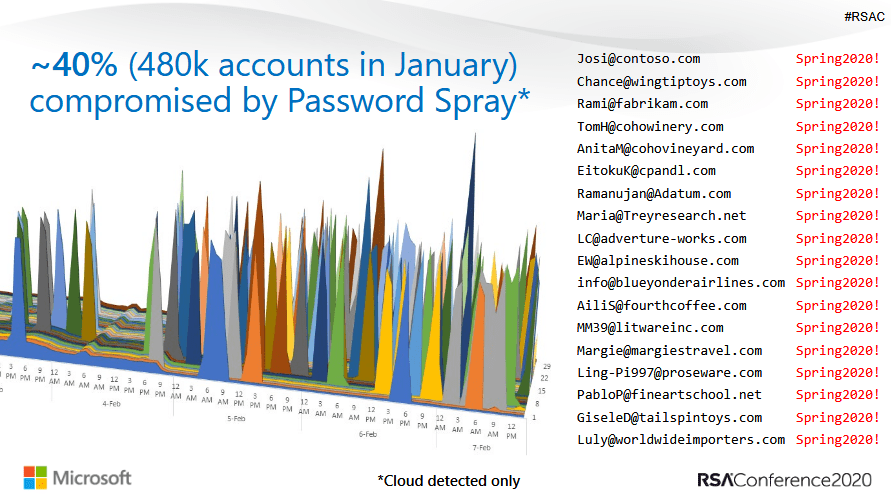
Microsoft engineers recently presented research at the RSA security conference indicating that 99.9% of compromised accounts aren’t using multi-factor authentication (MFA). This statistic alone illustrates the enormous potential for MFA to mitigate account breaches when passwords are either guessed or exfiltrated.

The same research indicated that about 0.5% of all accounts are compromised on a monthly basis, with approximately 1.2 million such accounts compromised in January of 2020. In that same January, 2020 data set, Microsoft claimed that only 11% of the accounts had MFA configured.
Account breaches

The leading cause of account compromise were password spraying, or what are commonly called brute force attacks, whereas multiple account passwords are guessed in rapid succession, using techniques that focus on the most commonly used passwords. Second to password spraying, were password replays, which involve re-using previously leaked or breached credentials. Thus re-using a username and/or password is also quite problematic for account security.

“We know that 60% of users reuse passwords. It’s super common,” said Lee Walker, Identity and Security Architect at Microsoft.

The resounding recommendation was enabling MFA across all accounts where it could be utilized. A recommendation that our security experts at Envescent strongly agree with as it is a powerful account risk mitigation strategy, reducing the potential for account breaches by up to 99.9%.

Posted in cybersecurity, risk management and tagged account compromise, hacking, Microsoft, phishing, RSA, security.

Need help with this?

Cybersecurity assessment is what we do for organizations in Arlington, Washington DC, Maryland, and worldwide.

Schedule a free consultationCybersecurity assessment →

Or call 703-486-0200. Weekdays 9–5 ET; after-hours and emergency rates are published in the service menu.

More guides All resources · Small business cybersecurity · AI for business · Compliance

Related reading

  • Virginia Data Breach Notification RequirementsNovember 4, 2026
  • What Is a Cybersecurity Assessment? Scope, Process, and OutputNovember 1, 2026
  • Prompt Injection: A Guide for Business LeadersOctober 28, 2026

Alexander G Chamandy founded Envescent in 1999. He leads cybersecurity assessments, incident response, and AI security engagements. Full bio

Post navigation

Previous articleEnvescent participates in Arlington Chamber-hosted cybersecurity panel
Next articleBusinesses should prepare for remote work for an extended duration

Recent Insights

  • Virginia Data Breach Notification Requirements
  • What Is a Cybersecurity Assessment? Scope, Process, and Output
  • Prompt Injection: A Guide for Business Leaders

Company Awards

Arlington Chamber Best Business Award WinnerArlington Chamber Best Business Award Winner

Strategic Partnerships


AWS Amazon Web Services Partner

Google Cloud Partner

Microsoft Partner
© 2026 Envescent, LLC : All rights reserved : Reach out : [email protected] : 703-486-0200
Envescent

Cybersecurity, AI risk, cloud, and compliance work for organizations in Arlington, Washington DC, Maryland, and worldwide.

703-486-0200[email protected]

1001 19th St N
Arlington, VA 22209

Services

  • Cybersecurity Services
  • AI Security Assessments
  • Incident Response
  • Penetration Testing
  • Compliance
  • Cloud Engineering
  • Training

Resources

  • Insights
  • Guides and resources
  • Small business cybersecurity
  • AI for business
  • AI readiness check
  • Security self-assessment

Company

  • About
  • How we work
  • Standards
  • Case studies
  • Service menu and rates
  • Contact

Service areas

  • All service areas
  • Alexandria, VA
  • Fairfax, VA
  • Falls Church, VA
  • McLean, VA
  • Great Falls, VA
  • Vienna, VA
  • Washington, DC
  • Bethesda, MD
  • Potomac, MD

© 2026 Envescent, LLC. All rights reserved.

  • LinkedIn
  • X
  • GitHub
  • Google
  • Yelp
  • Privacy
  • Terms
Back To Top